
The Alfabet SCIM Management application has been updated to include new capabilities.
Alfabet SCIM application delivery de-coupled
The delivery of the Alfabet SCIM application has been decoupled from the core Alfabet release cycle. This enables updates and enhancements to the Alfabet SCIM application to be made available immediately to customers, regardless of the release version they are using. The Alfabet SCIM application is now delivered as a separate download on the download page, allowing customers to benefit from the latest identity provisioning capabilities without requiring an upgrade of the core platform. The current version of the Alfabet SCIM application is 2.1.
Single sign-on support for Alfabet SCIM application
To enhance security and simplify user authentication, Single Sign-On (SSO) has been introduced as the authentication mechanism for accessing the Alfabet SCIM application. This enables users to authenticate through their organization's identity provider, providing a more secure and streamlined sign-in experience while supporting centralized access management and authentication policies.
Enhanced security with two-factor authentication
Two-factor authentication (2FA) has been introduced for all central administrative and configuration processes in the user interface of the Alfabet SCIM application. Even during an active session, users must provide a verification code generated by their authenticator application before accessing sensitive management functions. As SCIM administration is a security-critical activity, this additional verification step helps protect against unauthorized access and session hijacking. By requiring strong authentication for privileged operations, the application ensures that active sessions cannot be misused by unauthorized individuals, further strengthening the security of identity provisioning and user management processes.
JSON Web Token (JWT) for connections to the identity provider
JSON web tokens are exclusively used for requests for user data to the identity provider. This requires setup of an API with an Audience claim for the registered application at the identity provider. The configuration of the access to the identity provider has changed. Configurations from prior releases are not valid any longer. The SCIM setup documentation has been updated with the required settings.
Enhanced troubleshooting with stored SCIM user data
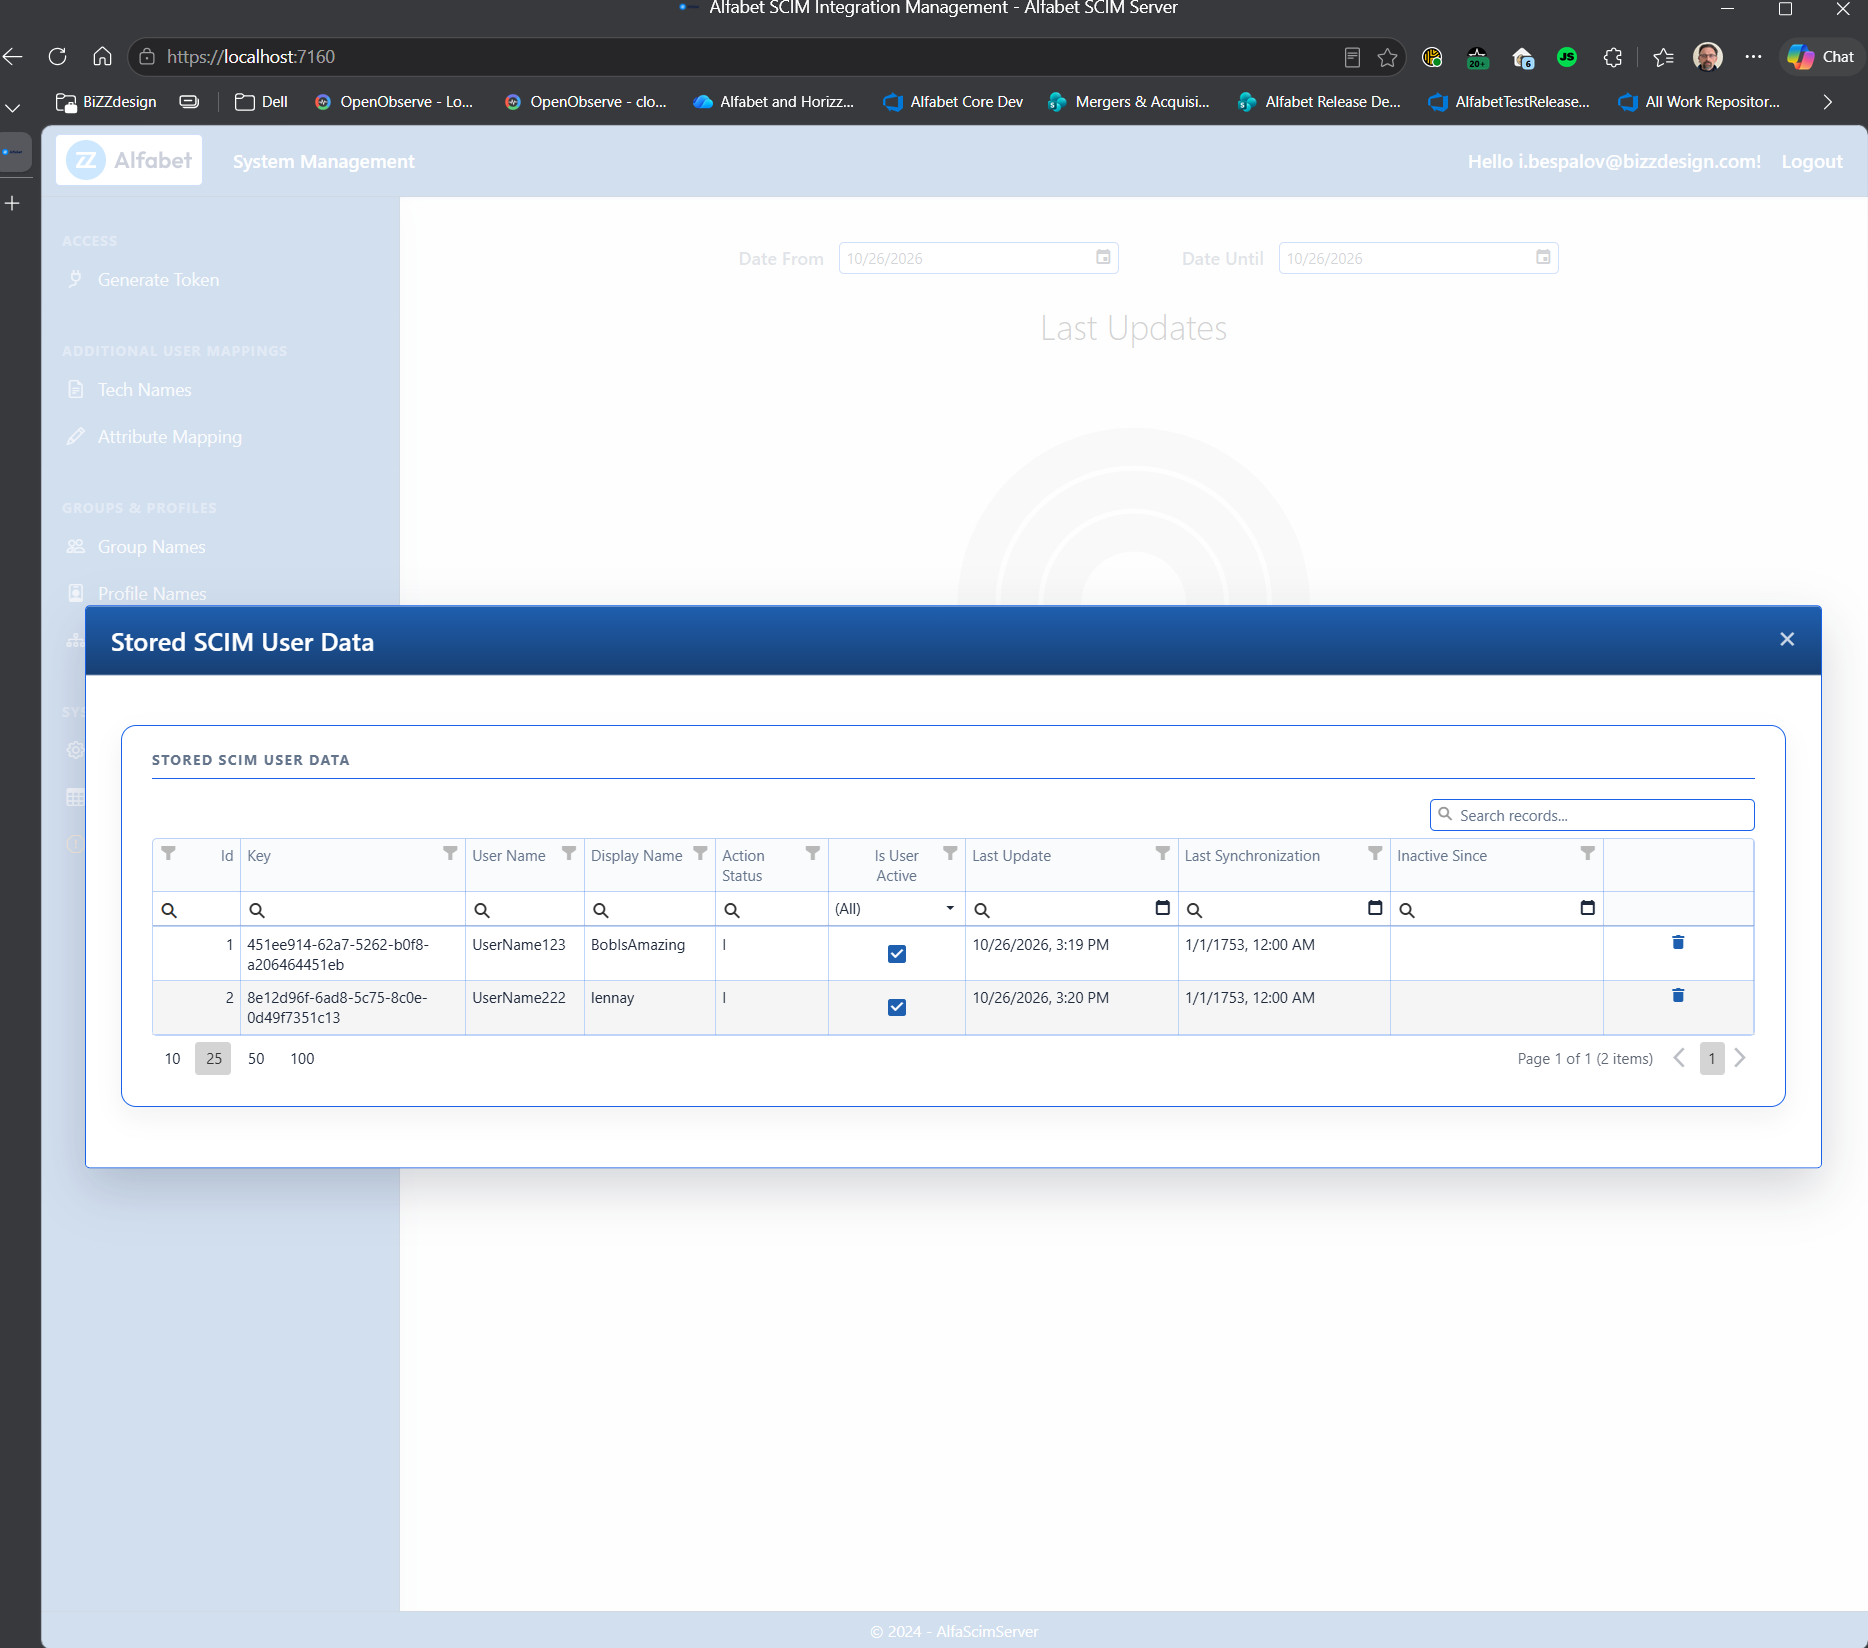
A new Stored SCIM User Data view has been added to the user interface of the Alfabet SCIM application. The view displays the user data stored in the Alfabet SCIM application's internal database, which is derived from information received from the configured identity provider. This capability helps administrators diagnose synchronization issues and identify problems that may result from inconsistent or conflicting user data.
Because the view exposes sensitive user information, its availability can be controlled through the Alfabet SCIM application settings. It is recommended that access to this view be enabled only for troubleshooting purposes when issues occur.
While the view includes functionality to remove user data from the internal database, customers should use it solely for diagnostic purposes and when requested by Alfabet Support. Any modification or correction of internally stored user data should be performed exclusively under the guidance of Alfabet Support to ensure data consistency and integrity.
Automatic certificate handling
It is no longer required to create certificates for the SCIM application manually. Instead, self-signed certificates are created automatically on first start-up of the Alfabet SCIM application with a validity of two years. When existing certificates have expired, they will automatically be substituted with new certificates.